The private key ensures solely you could get through the entrance door. In the case of encrypted messages, you employ this private key to decrypt messages. They work on the public key cryptography structure, barring one small caveat. Typically, the uneven key system uses a public key for encryption and a private key for decryption. However, when coping with digital signatures, it’s the other.
It Is a secret string of characters that you want to never share with anyone. The following illustration reveals a CA hierarchy with a certificates chain leading from an entity certificate by way of two subordinate CA certificates (CA6 and CA3) to the CA certificate for the foundation CA. Certificates authority (CA) hierarchies are mirrored in certificate chains. A certificate chain traces a path of certificates from a department in the hierarchy to the root of the hierarchy. Completely Different vendors often use completely different and sometimes proprietary storage codecs for storing keys.
How Encryption Consulting Helps

By signing the message with the sender’s private key, this ensures https://214rentals.com/the-pen-test-is-designed-to-simulate-the-actions-of-hackers.html for the recipient that the message actually did come from the sender. In the past, secure encrypted communication required that the people first trade keys by a safe means such as paper key lists transported by a trusted courier. The Diffie–Hellman key trade method permits two parties that have no prior data of each other to jointly establish a shared secret key over an insecure channel by establishing a shared secret. To create a digital signature, Bob digitally signs his email to Alice utilizing his private key.
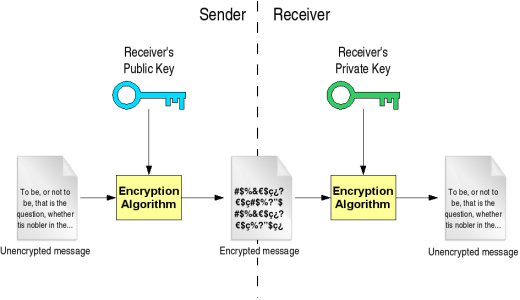
Since the general public key can solely be used to decrypt messages signed with Alice’s personal key, we are in a position to trust that Alice was the author of the original message. Bob encrypts a plaintext message with Alice’s public key, then Alice decrypts the ciphertext message with her personal key. Since Alice is the only one with access to the private key, the encrypted message can’t be learn by anyone besides Alice.
- However, as is the case with the factorization problem, therehave been extensive assaults towards the RSA drawback, and no betterattack than factorization of \(N\) has been discovered.
- Now that you have some safety fundamentals under your belt, it might be time to audit your password necessities or implement two-factor authentication.
- Businesses deal with giant quantities of belongings, making the safety of personal keys a critical concern.
- With this advanced cryptographic system, messages and attachments are encrypted on the sender’s device using the recipient’s public key.
Rsa Algorithm: Secure Your Knowledge With Public-key Encryption

Public-private key encryption is a technique of cryptology that makes use of two associated keys to protect important information. One of the keys is a public key that’s known to everybody and the second key is a non-public key that’s only recognized to its owner. These, two unique cryptographic keys work collectively to protect digital data from prying eyes and hold your e mail encrypted. For example, in safe e mail communication, a sender encrypts the message using the recipient’s public key. Only the recipient can decrypt this message with their personal key, ensuring the message’s confidentiality. Alice encrypts a plaintext message with her non-public key, then sends the ciphertext to Bob.
What Are Public And Private Keys?
When X wants to speak with Y, X makes use of Y’s public key to encrypt the message; that is attainable as a outcome of Y shares her public key to X. In a decentralized system like Bitcoin, trust and safety usually are not enforced by a central authority but by cryptography. The computational infeasibility of deriving the personal key from the public key’s what makes Bitcoin proof against fraud and hacking attempts. The mathematical complexities of the ECC algorithm make it virtually inconceivable to reverse-engineer the personal key from the basic public key. However, the Achilles’ heel lies within the source of randomness.
Leave a Reply